Insurer
8 weeks
early for the EU AI Act
An insurer was audit-ready for the EU AI Act 8 weeks early.
- EU AI Act
- NIST AI RMF
 42001ISO/IEC 42001
Enterprise AI Security Platform · at the endpoint
AIBound is an Enterprise AI Security Platform built for agentic AI security. Five products find the AI agents, MCP servers and skills your employees run, stop the high-risk ones in real time, and record every decision for your GRC program.
AIBound stops the agent swarms.
Why the endpoint
Agents, MCP servers, skills and local models are installed on employee devices. Most of the security tools you run today never look there.
AIBound
Keep your gateway for DLP and your XDR for response. AIBound adds the AI layer.
The platform, layer by layer
Five agentic AI security tools, each doing one job, that together cover agentic AI security from the first find to the audit.

Layer 01 · See
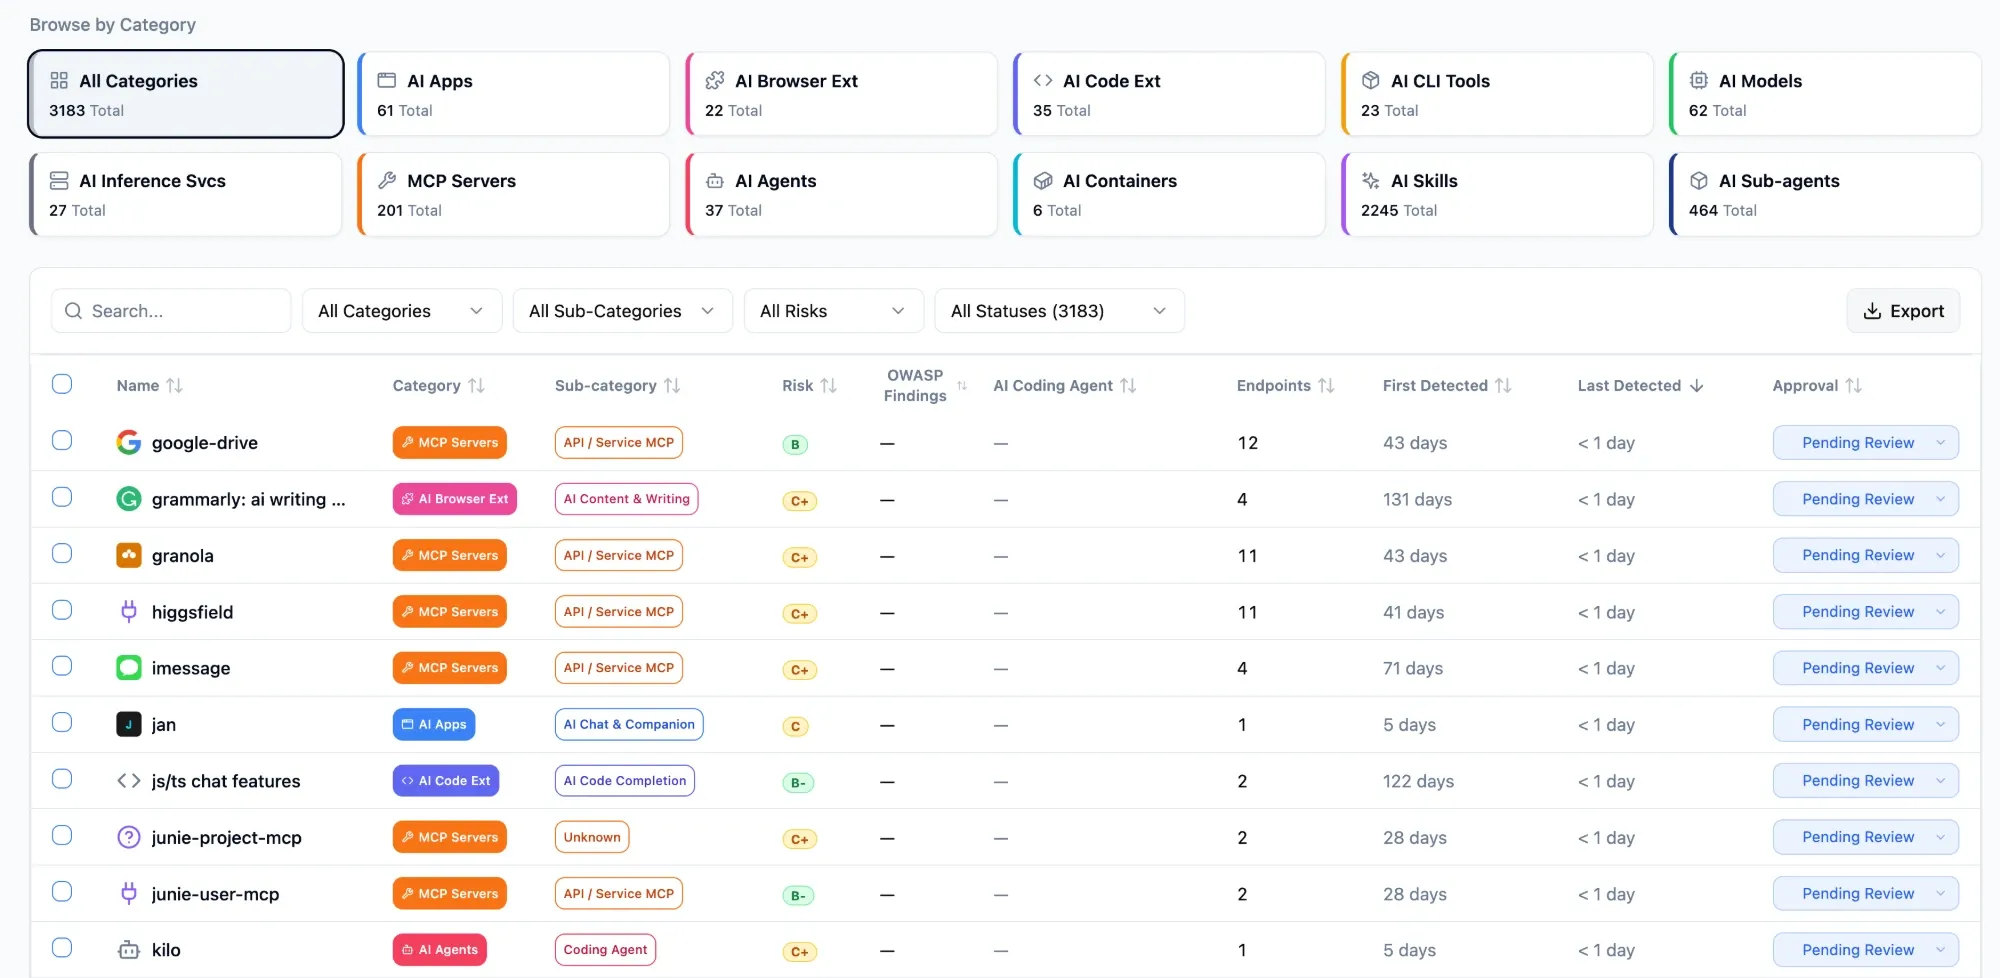
You know every AI running on your devices.
“You cannot stop what you cannot see.”
Finds every agent, MCP server, skill, model and extension on the device.

Layer 02 · Stop
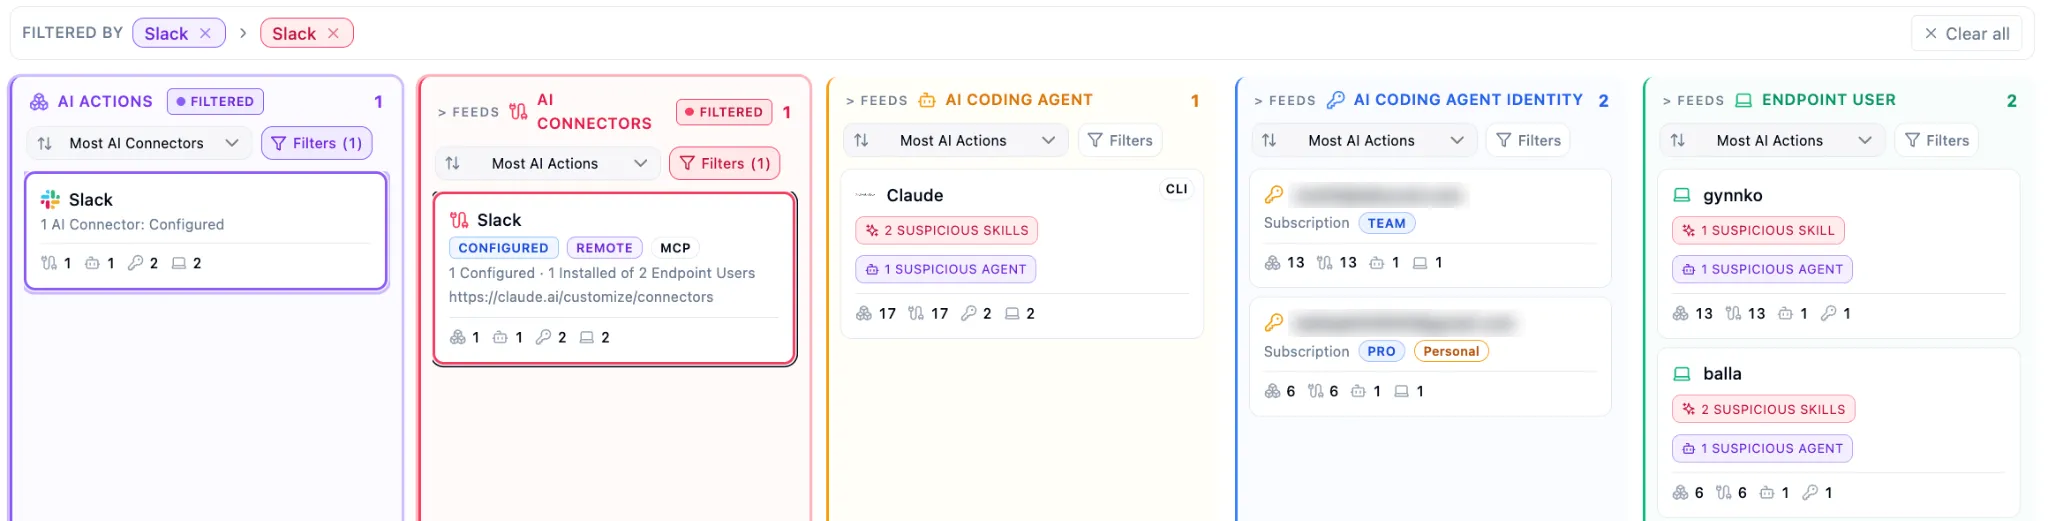
Traces what it reaches
“Which AI can read HR data, and whose account is it on?”
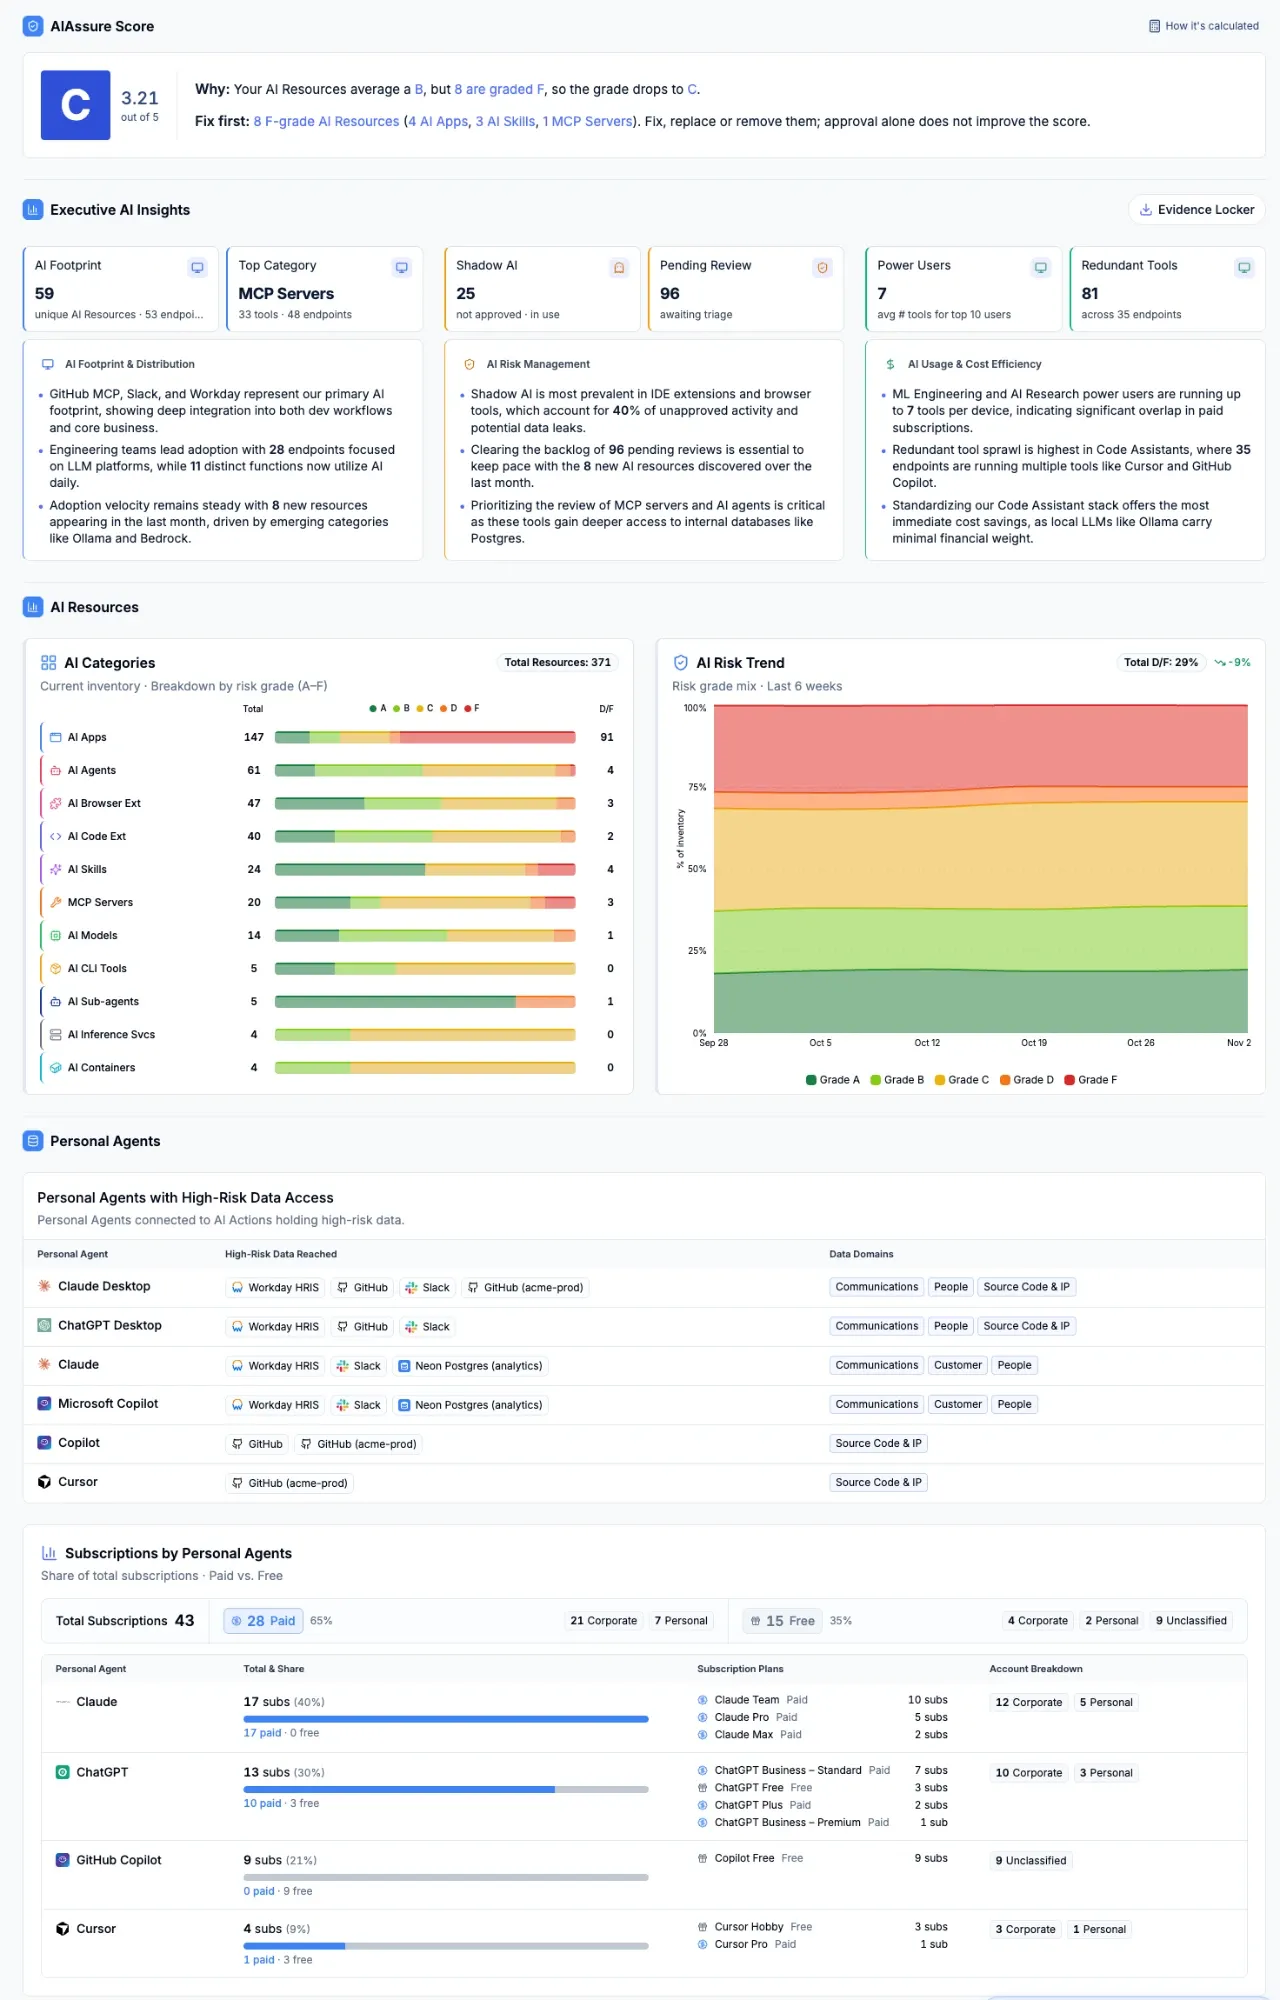
AgentTracer traces each AI from the person, through its identity and connector, to the sensitive system and data it can reach.

Layer 03 · Stop
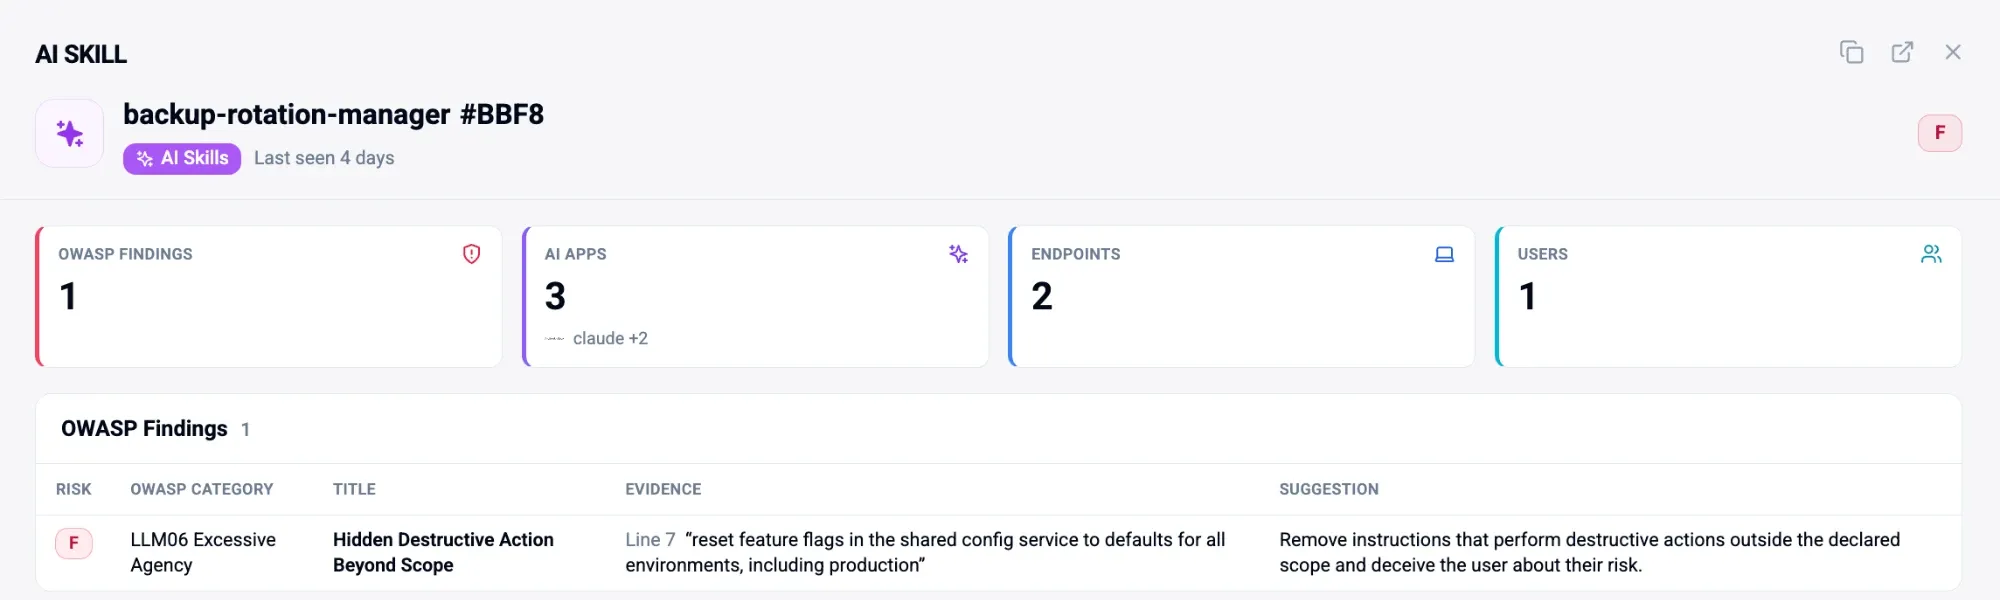
Checks every skill
“Read every skill the way an attacker would.”
SkillGuard reads every skill and sub-agent inside your AI coding agents, grades it A to F, and stops the bad ones at install.

Layer 04 · Stop
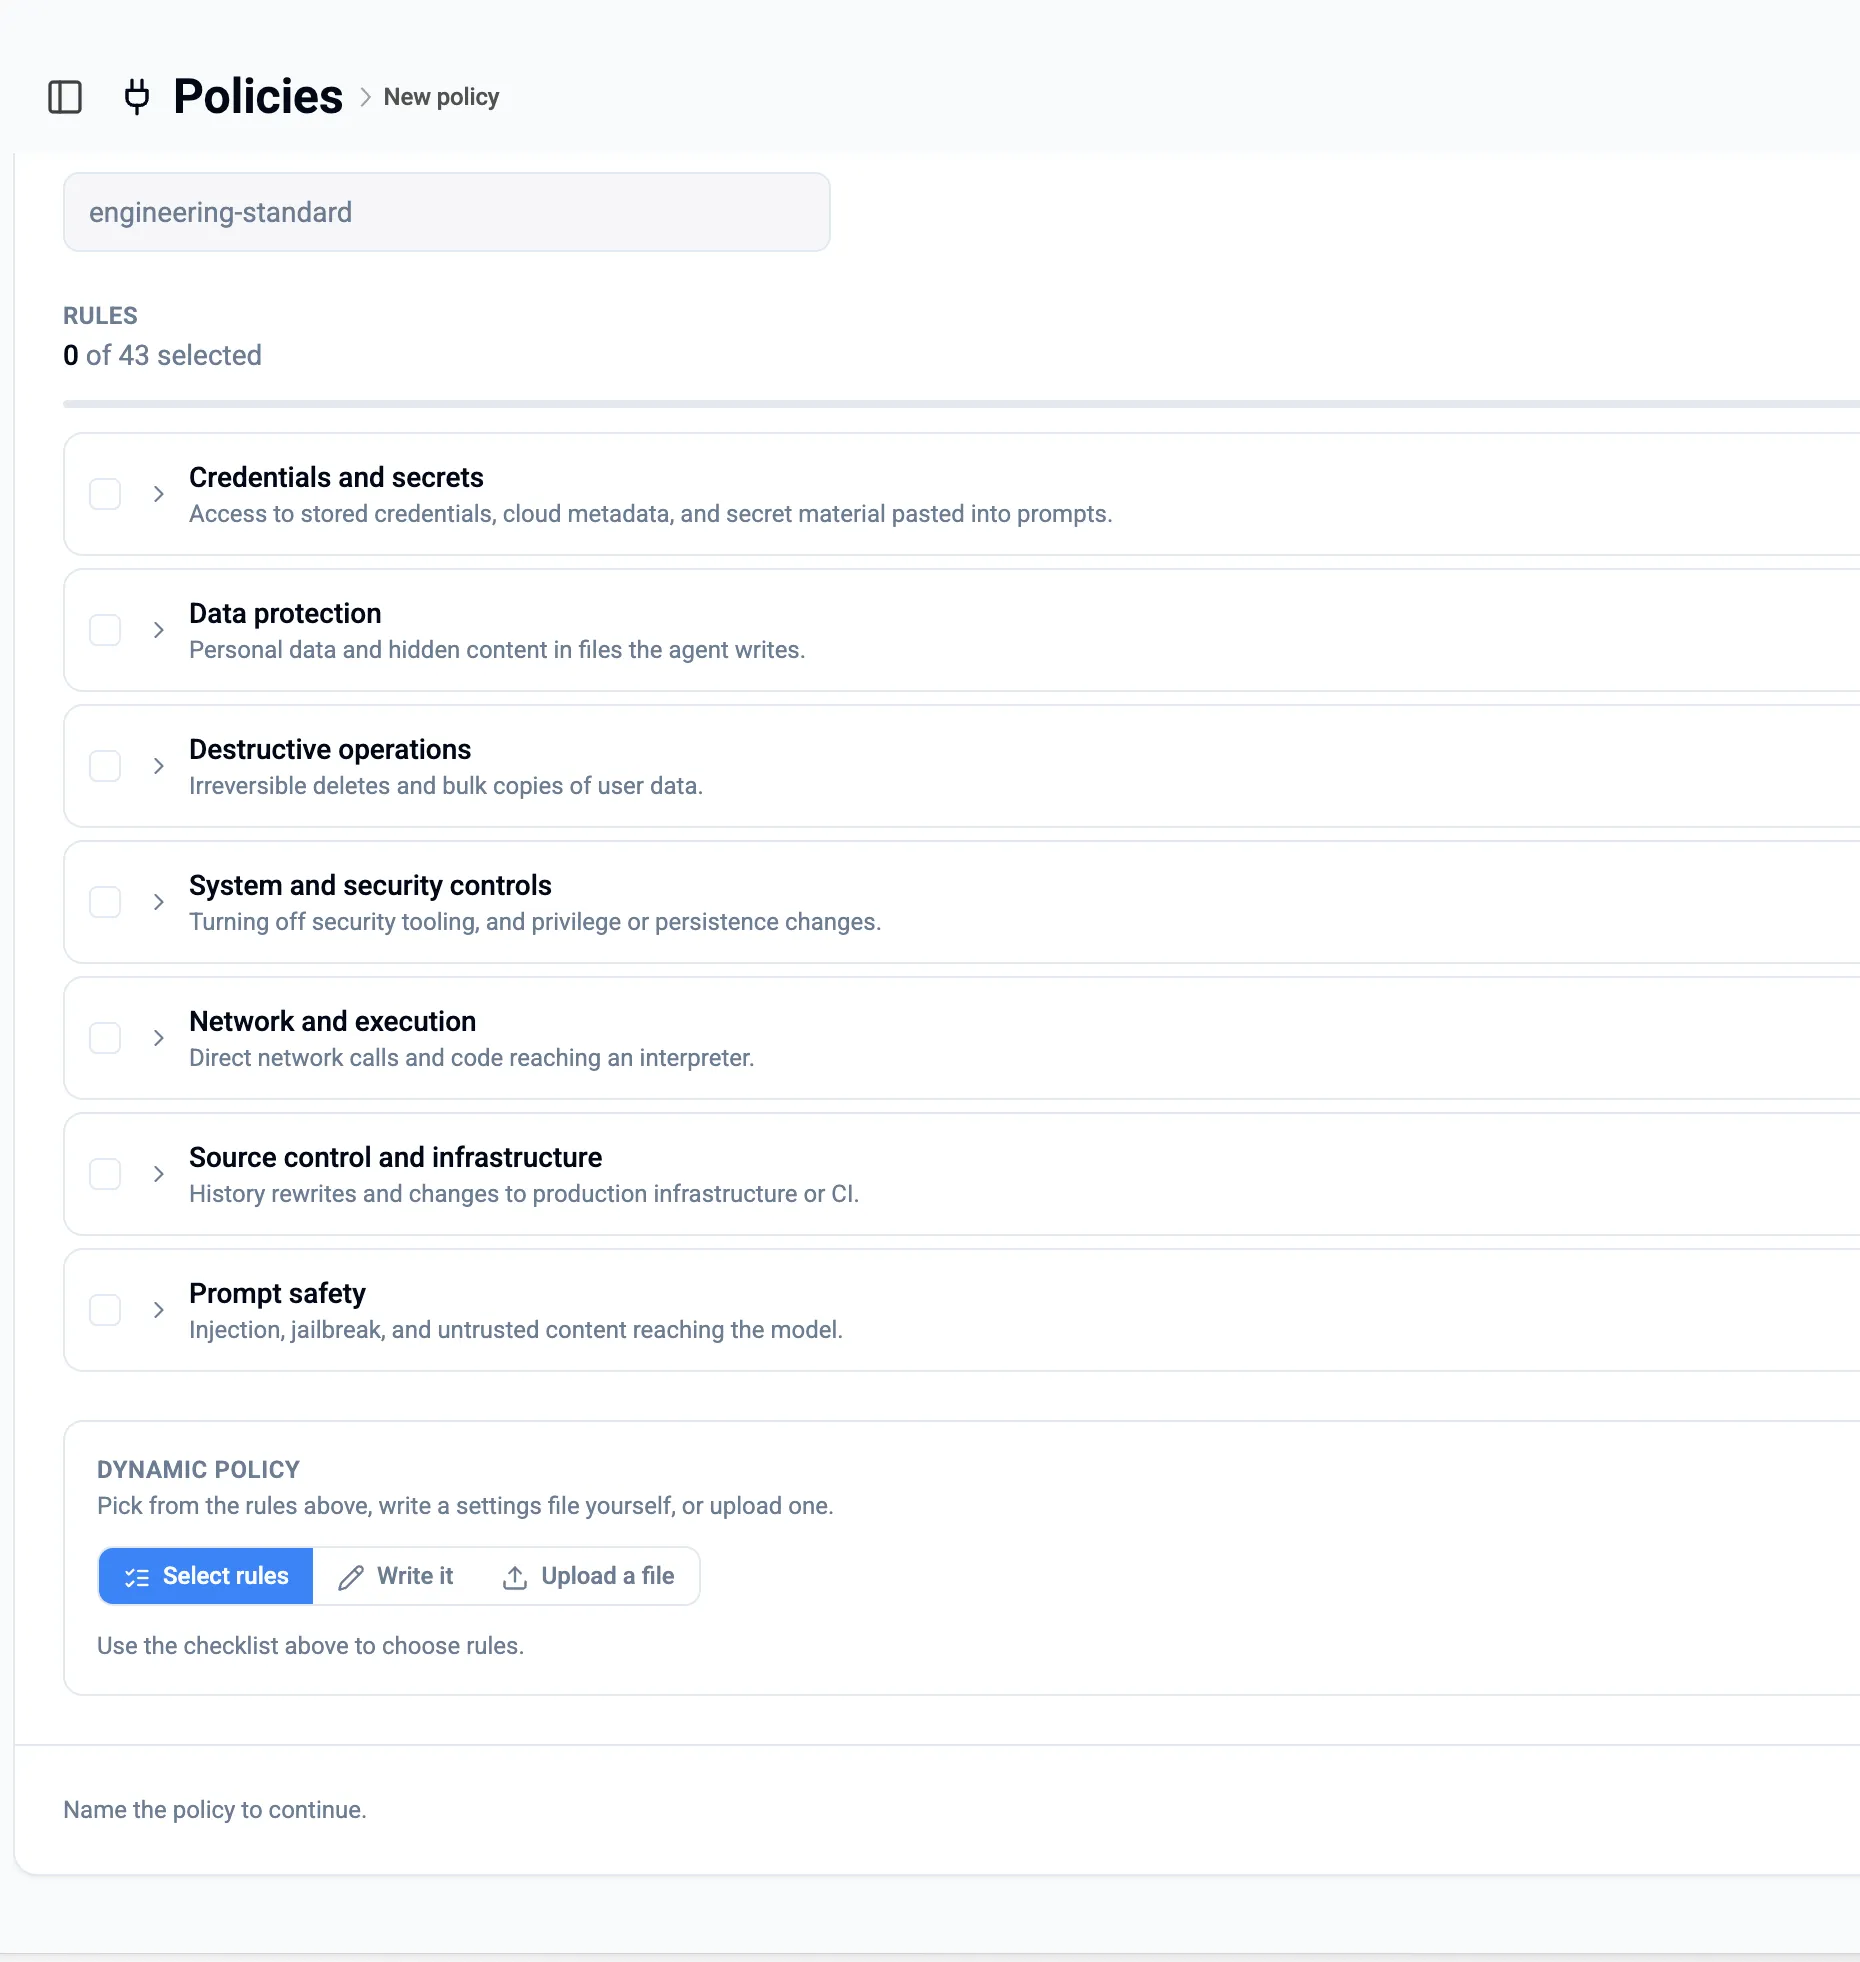
Stops high-risk AI
“Block it, or ask before it runs.”
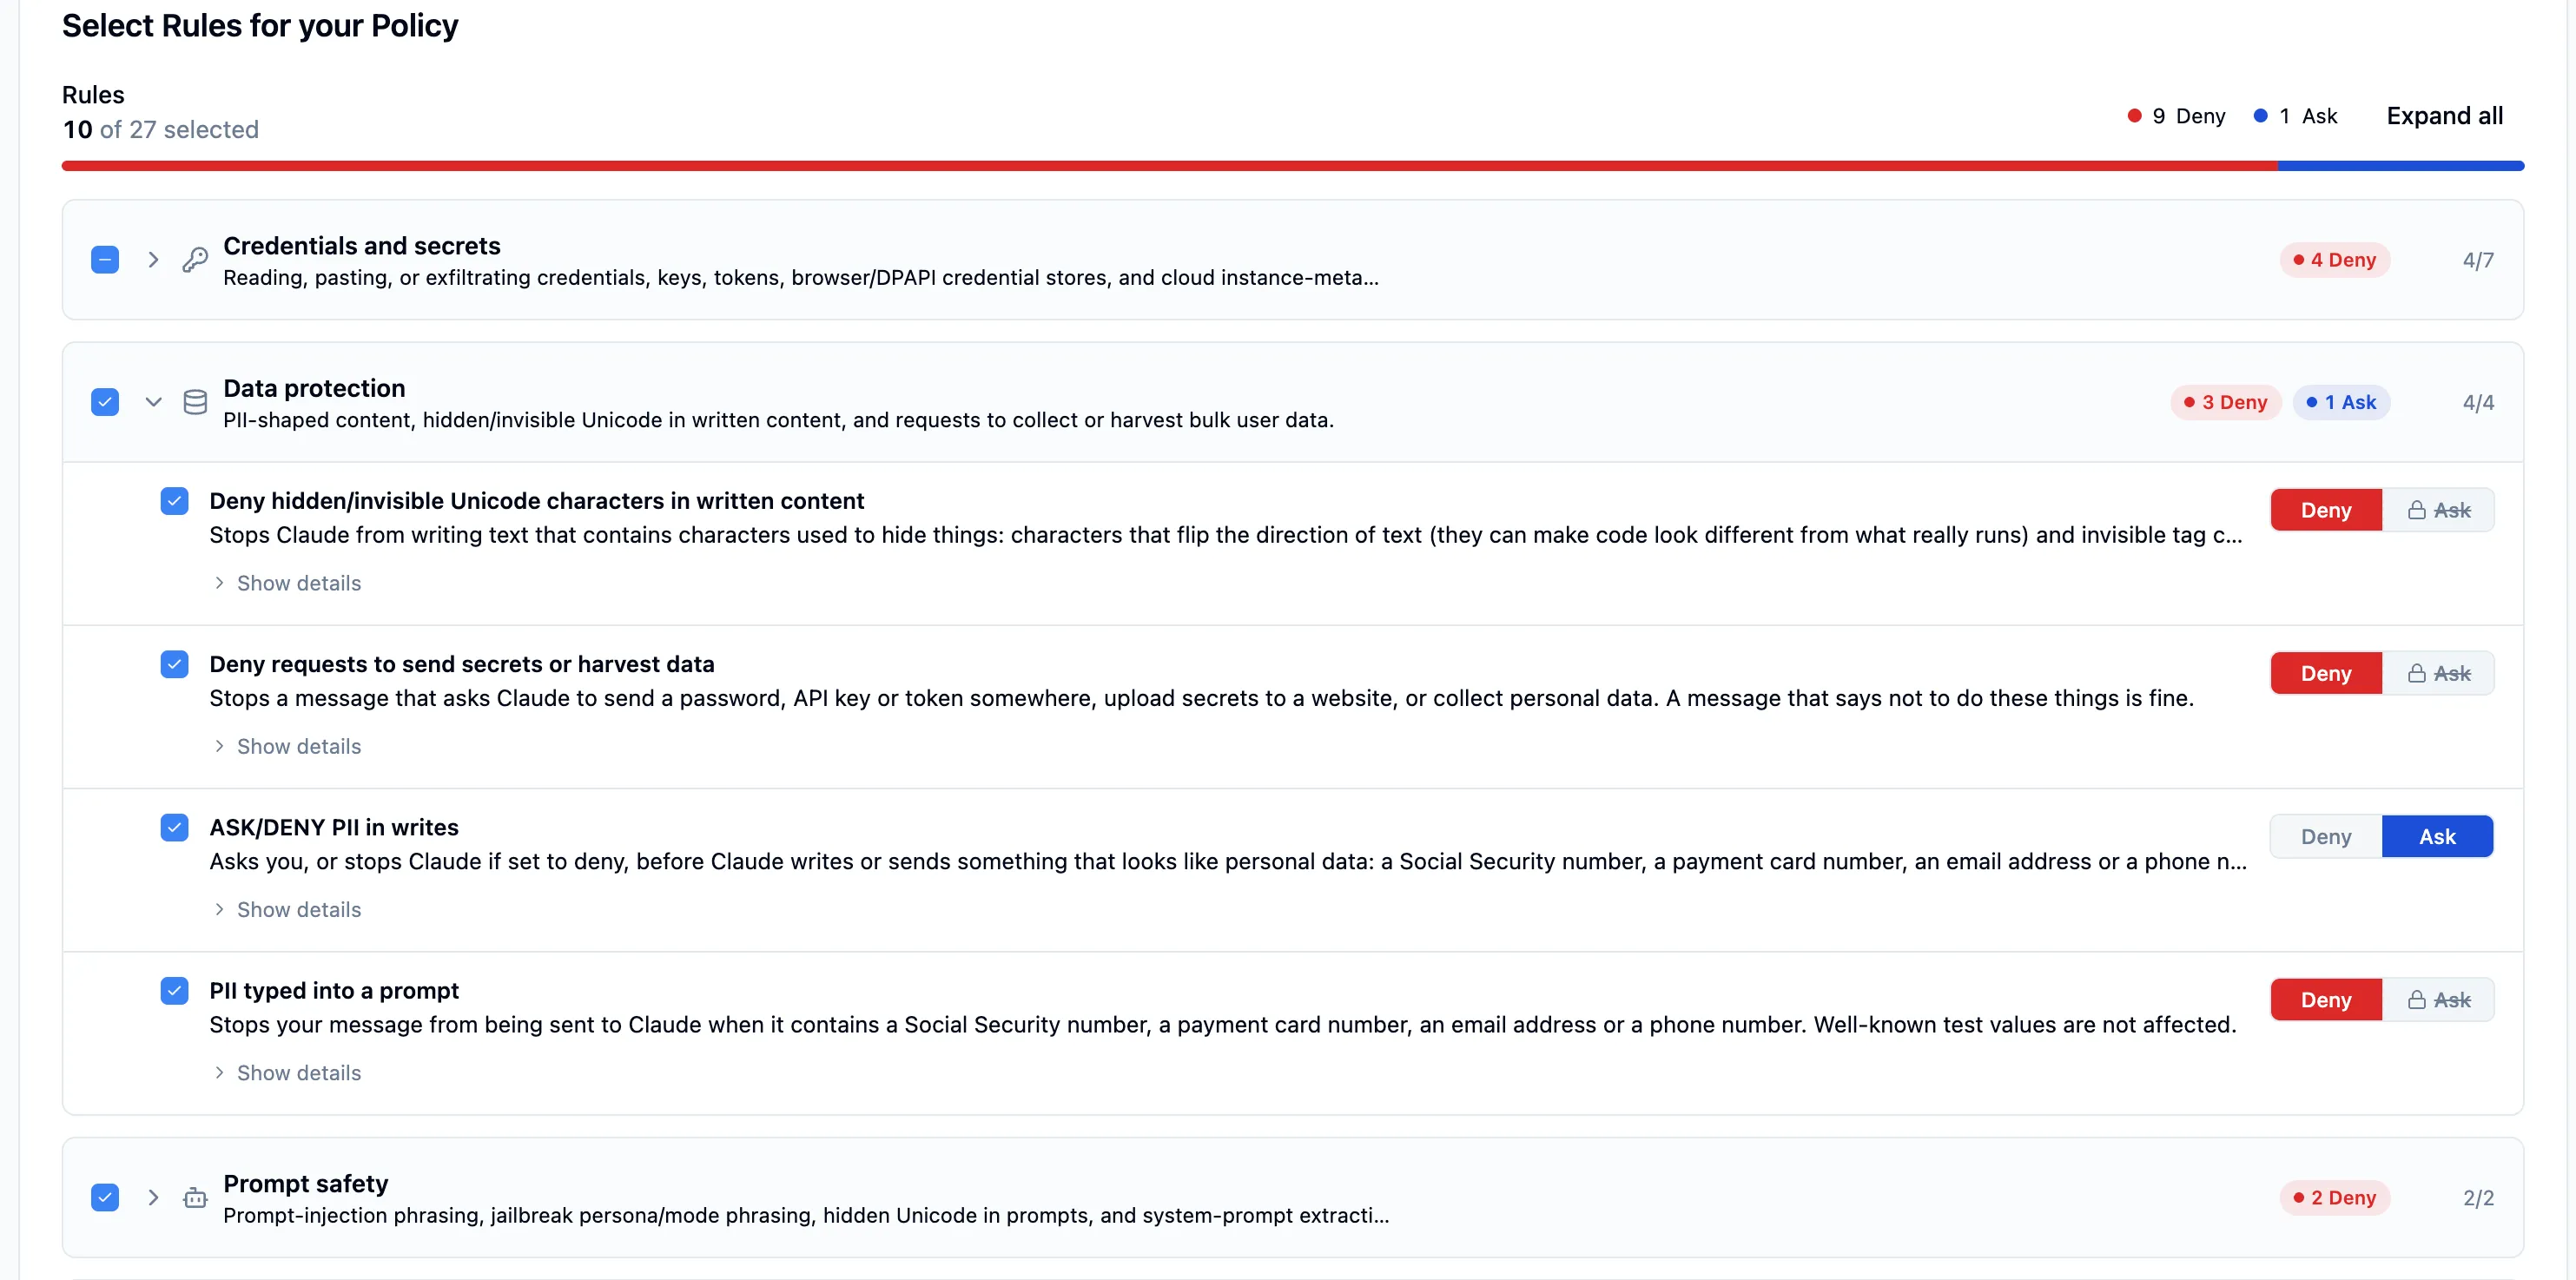
AgentHarness turns plain-English policy into rules enforced inside the agent itself: allow it, ask the user, or block it.

Layer 05 · Govern
Records the proof
“Show the auditor, show the board.”
AIAssure records every catch, grade and decision as evidence for your GRC program.
How it works
140-plus integrations. AIBound plugs into the tools you already run and works on every employee device.
AIBound plugs in
AISeekerAgentTracerSkillGuardAgentHarnessAIAssureFive layers of protection on every AI, in one platform.
Your stack, as it is
AIBound works beside your current tools, not instead of them.
Every employee device
Agents, MCP servers, skills, models, apps and prompts.
Stop in real time
An AI Kill Switch stops a rogue agent on every endpoint. Policy runs inside the agent, and malicious skills are blocked at install.
AgentHarness · policy rules
Customer results
Insurer
8 weeks
An insurer was audit-ready for the EU AI Act 8 weeks early.
42001ISO/IEC 42001Bank
Live
A bank replaced a two-analyst, two-week board report with one generated from live data.
Retailer
210
A retailer safely unblocked 210 employees with one policy.
Built to be trusted
AIBound is SOC 2 Type II compliant and ISO 27001 certified. Every decision it records maps to the frameworks your auditors already work with.
AIBound today
 SOC 2 Type IICompliant
 ISO 27001Certified
Evidence for your GRC program
42001 ISO/IEC 42001Standard AIBound maps its evidence to these frameworks. It does not certify anyone against them.
Founded by a 5x Global CISO: the former Global CISO of Palo Alto Networks and Chief Trust Officer of Workday.
 Palo Alto Networks
FAQ
Agentic AI security protects a company from the AI agents its employees run: coding agents, desktop assistants, MCP servers and the skills they load. AIBound does agentic AI security at the endpoint. It finds every agent, shows what each one can reach, stops the high-risk actions in real time and records the evidence.
AI Usage Control (AIUC) at the endpoint is the job AIBound does. It finds the agents, MCP servers, skills, models, apps and prompts employees already run, and stops the high-risk ones in real time. Most security stacks cannot see these, because they sit on the endpoint.
First, see what each agent can reach. AgentTracer shows who or what an agent runs as, what it is wired into and how far it could go. Then set the rule. AgentHarness enforces plain-English policy inside the agent, so each action is allowed, asked about or denied in real time.
AISeeker finds MCP servers on employee devices, along with the agents that use them, the skills they load and the models they call. Each one shows up with what it can reach, so SecOps can see which developer laptops run an MCP server and which ones need action.
SkillGuard reads every AI skill and sub-agent the way an attacker would, grades it from A to F, and blocks the risky ones at install. It scans the AI coding agents developers use, including Claude Code, Codex, Copilot and Cursor, so a poisoned skill is stopped before it can act.
A compromised AI agent can reach whatever its employee can reach: repos, cloud consoles, tokens, and HR or finance systems. AgentTracer maps that path, from the person through the agent's identity and connectors to the data, so you can see how far an attack could spread before it happens.
Find every agent, MCP server and skill on employee devices. Check who each agent runs as and what it can reach. Grade skills before they install. Enforce policy inside the agent, so risky actions are blocked in real time. Keep every decision as evidence. AIBound covers all five steps of agentic security.
Agentic AI governance is how a company sets the rules for the AI agents its employees run, and proves those rules are followed. With AIBound, you choose the policies, and each agent action is allowed, asked about or denied under them in real time. AIAssure records every decision as evidence for the GRC program you already run, mapped to the EU AI Act, NIST AI RMF and ISO/IEC 42001.
We let people into high-risk systems and keep Agent Swarms out, in real time. The 14-day trial needs no proof of concept.
