
01
Personal accounts in corporate systems
An employee connects a personal login to an AI assistant that touches a corporate system. Nothing in your stack ties the two together.
Layer 02 · Stop
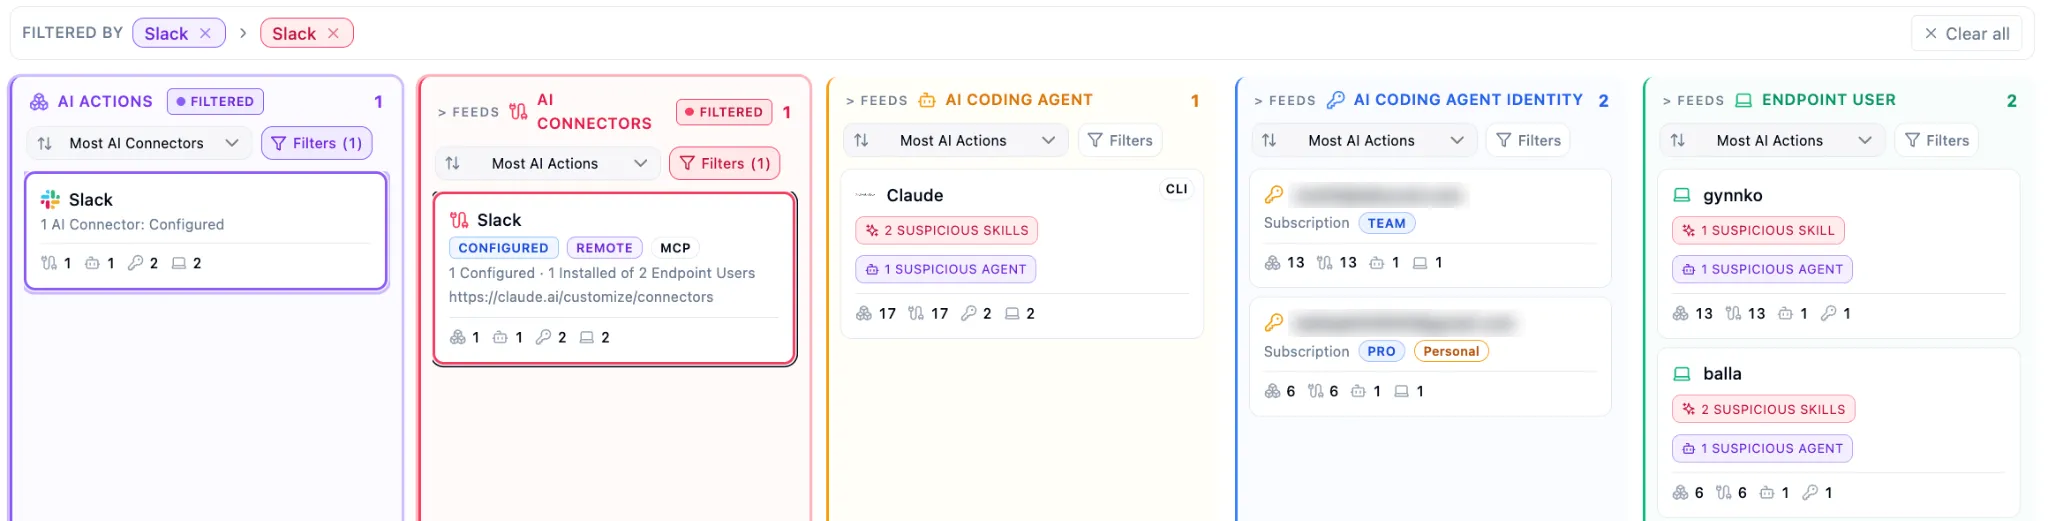
AgentTracer maps who or what each AI agent runs as, which sensitive systems it is wired into, and how far a compromised agent could reach. It traces every AI from the employee, through its account and connector, to the data it can touch, so you can decide what to allow, ask about or deny.
The problem
Agents inherit whatever their employee can reach. Few security teams can say which agent holds which login.
What it does
AgentTracer maps each AI back to a person, an account and the systems behind it. It maps and does not block. What you learn becomes a rule you can enforce with AgentHarness.
How it works
IT pushes the AIBound Secure Client to employee devices like any other app. There is no new agent to run.
It ties every AI on a device to a person, an account, its connectors and the systems behind them.
Set a policy to allow, ask or deny. AgentHarness enforces it inside the agent, and AIAssure keeps the evidence.
What you see
AgentTracer traces each AI from the person to the data it can reach.
Who uses it
Four roles use AgentTracer to answer one question: what can this AI reach?
What this looks like in practice
We didn't know 47 employees were running it. AIBound flagged it and blocked it the same afternoon.
A CISO at a European bank.
FAQ
AI agent identity is who or what an AI agent runs as: the employee, the account it signs in with and the connectors that link it to other systems. AgentTracer maps AI agent identity for every agent on employee devices, including personal accounts wired into corporate systems, so you can see what each one is allowed to touch.
First, see what each agent can reach. AgentTracer maps who or what an agent runs as, what it is wired into and how far it could go. Then set the rule. AgentHarness enforces plain-English policy inside the agent, so each action is allowed, asked about or denied in real time.
A compromised AI agent can reach whatever its employee can reach: repositories, cloud consoles, tokens, and HR or finance systems. AgentTracer maps that path, from the person through the agent's account and connectors to the data, so you can see how far an attack could spread before it happens.
No. AgentTracer maps identity and reach, and it does not block. Blocking happens elsewhere on the platform: SkillGuard blocks malicious skills at install, and AgentHarness enforces your policy inside the agent, so each action is allowed, asked about or denied in real time.
No new agent. IT pushes the AIBound Secure Client to employee devices like any other app, and install takes 15 minutes. It collects tool metadata only, with no PII or PHI. AgentTracer then maps what each AI runs as and what it can reach, and you see the results in real time.
AIBound blocks the high-risk AI on every employee device, in real time. The 14-day trial needs no proof of concept.
