
Solution · Govern
AI compliance evidence for the GRC program you already run
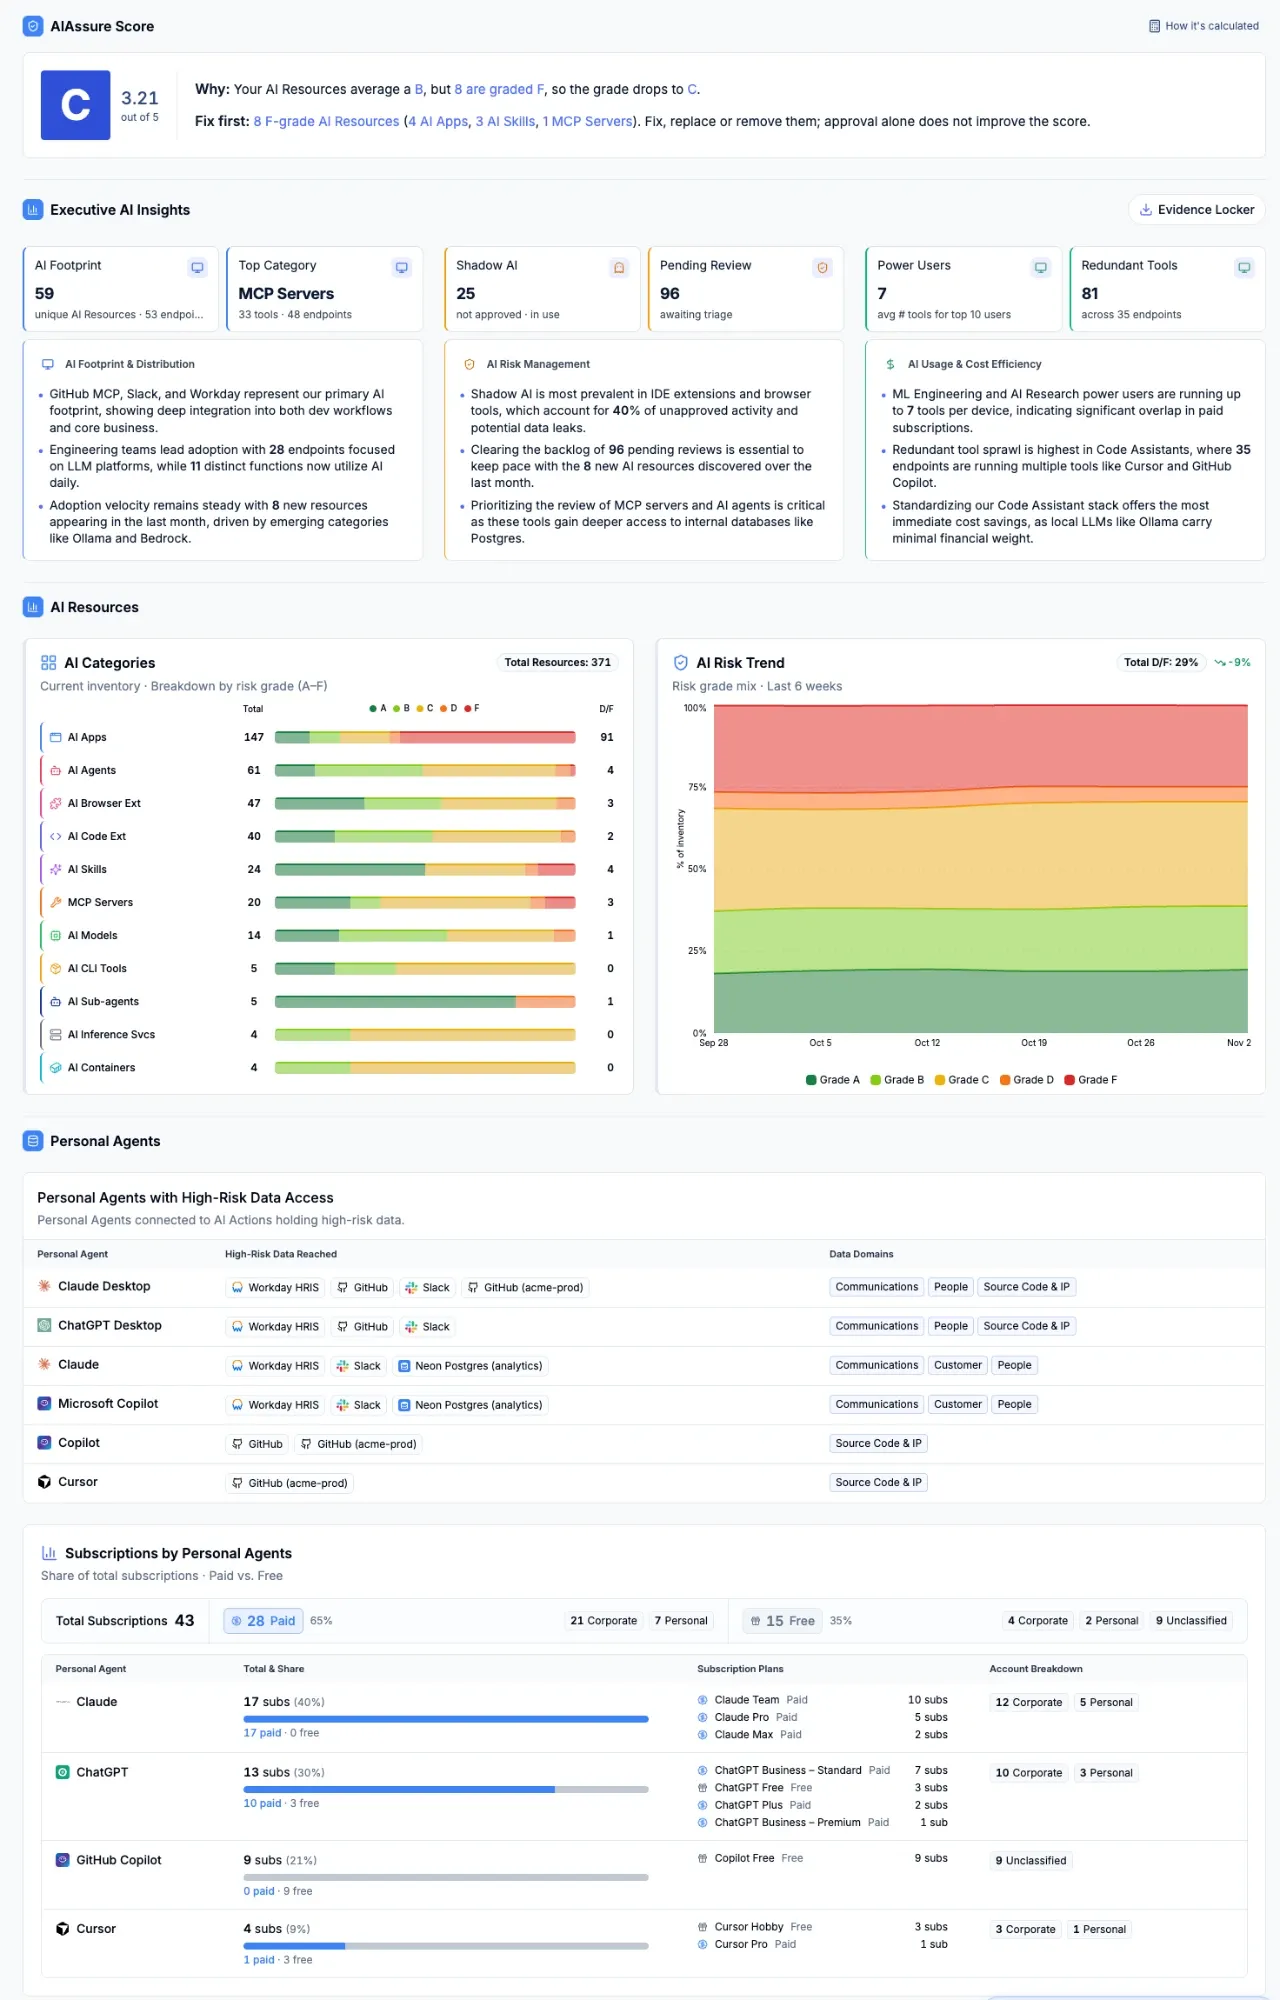
AIBound is an Enterprise AI Security Platform. While it finds and stops AI on employee devices, it records every grade and decision as evidence. AIAssure maps that evidence to the EU AI Act, NIST AI RMF and ISO/IEC 42001 and feeds your GRC program, so it stays current without a second governance system.
The problem
How do you prove to an auditor which AI your company runs?
The auditor asks for your AI list, your risk assessment and your oversight controls. Most teams answer from a spreadsheet built by hand.
How we solve it
AI compliance evidence built from live data
The evidence comes from the same platform that finds and stops the AI, so it is never a separate project.
-
Find the AI on employee devices
AISeeker finds the agents, MCP servers, skills and models your employees run. Install takes 15 minutes.
-
Record every grade and decision
Each finding and each allow, ask or deny decision is kept, with the evidence behind it.
-
Map it and export it
AIAssure maps each finding to the three frameworks and exports it for the auditor or the board.
What you get
Evidence your GRC team can use as it is
Findings and decisions arrive already mapped. AIBound maps its evidence to these frameworks. It does not certify anyone against them.
EU AI Act timetable
The EU AI Act timetable, as it stands today
The high-risk dates moved in July 2026. Here is what applies when, checked against the Official Journal on 16 November 2026.
| Date | What applies | What it means for the AI your employees run |
|---|---|---|
| 2 February 2025 | The bans on prohibited AI practices, and the duty to support AI literacy. | Know which AI your employees use, so you can show none of it is a banned use. |
| 2 August 2025 | Rules for general-purpose AI models, the governance bodies and the penalties. | The fines are live. Model makers carry the model rules. You carry how your employees use the tools. |
| 2 August 2026 | The Act applies in general, including the transparency duties in Article 50. | Tools that generate content must say it is AI. Know where your employees use them. |
| 2 December 2026 | New bans on AI that makes intimate images of real people without consent, and on child sexual abuse material. Generative tools already on the market have until this date to mark their output. | Low risk for most companies. Name these uses as off limits in your policy. |
| 2 December 2027 Moved from 2 Aug 2026 | The high-risk rules for the listed uses in Annex III, such as hiring, credit and education. | If employees use AI in these uses, keep a record of the system, who uses it and the decisions you made. |
| 2 August 2028 Moved from 2 Aug 2027 | The high-risk rules for AI built into regulated products. | Mostly for product makers. Employee AI is rarely here. |
The delay moves the dates, not the duties.
The work you will have to show later is the work of today: what AI runs, who uses it and what you allowed.
Source: Regulation (EU) 2024/1689, Article 113, as amended by Regulation (EU) 2026/1744 (Official Journal, 24 July 2026). Checked on EUR-Lex on 16 November 2026.
What this looks like in practice
An insurer has real-time compliance with the EU AI Act.
A bank replaced a two-analyst, two-week board report with one generated from live data.
Which products
Which products do this
Three AIBound products turn AI activity into evidence.


FAQ
Frequently asked questions
What is AI compliance evidence?
AI compliance evidence is the record that shows an auditor which AI your company runs, how risky it is and what you decided about it. AIBound produces it from the AI on employee devices, so the record covers what is really installed, and it maps each item to the frameworks auditors ask about.
Does AIBound make us compliant with the EU AI Act?
AIBound helps you get compliant. It finds the AI your employees run, tags each finding to the EU AI Act article it relates to and keeps the decisions you make. The company still owns its compliance. AIBound supplies the evidence that GRC and legal teams work from.
Does AIBound certify us for ISO/IEC 42001 or NIST AI RMF?
No. AIBound maps its evidence to NIST AI RMF and to ISO/IEC 42001 and helps you get certified for ISO/IEC 42001. It does not certify anyone against either framework. For NIST AI RMF, evidence is mapped to the Govern, Map, Measure and Manage functions.
How does this fit the GRC program we already run?
AIBound feeds it. The evidence is mapped to the frameworks your GRC team already works with and can be exported for the auditor or the board. You keep your own governance process. AIBound adds live evidence from employee devices, so the program stays current without a second system.
Is AIBound a governance platform?
No. AIBound is an Enterprise AI Security Platform. It finds the AI your employees run, stops the high-risk ones in real time and records every decision. That record becomes the evidence your governance program runs on. You keep your existing GRC tools and add the AI evidence they lack.
More solutions
