
Solution · Stop
AI DLP: stop sensitive data leaving through AI agents
AI agents can read secrets, customer data and source code, and send them anywhere their employee can. AIBound enforces policy inside the agent, on the device. A credential read is denied, a destructive command is blocked, and personal data is kept out of prompts and tool output, in real time.
The problem
How do you stop sensitive data leaving through AI?
Data loss prevention was built for email, files and web uploads. It was not built for an agent that reads a secret and acts on it in one step.
How we solve it
AI DLP inside the agent, on every action
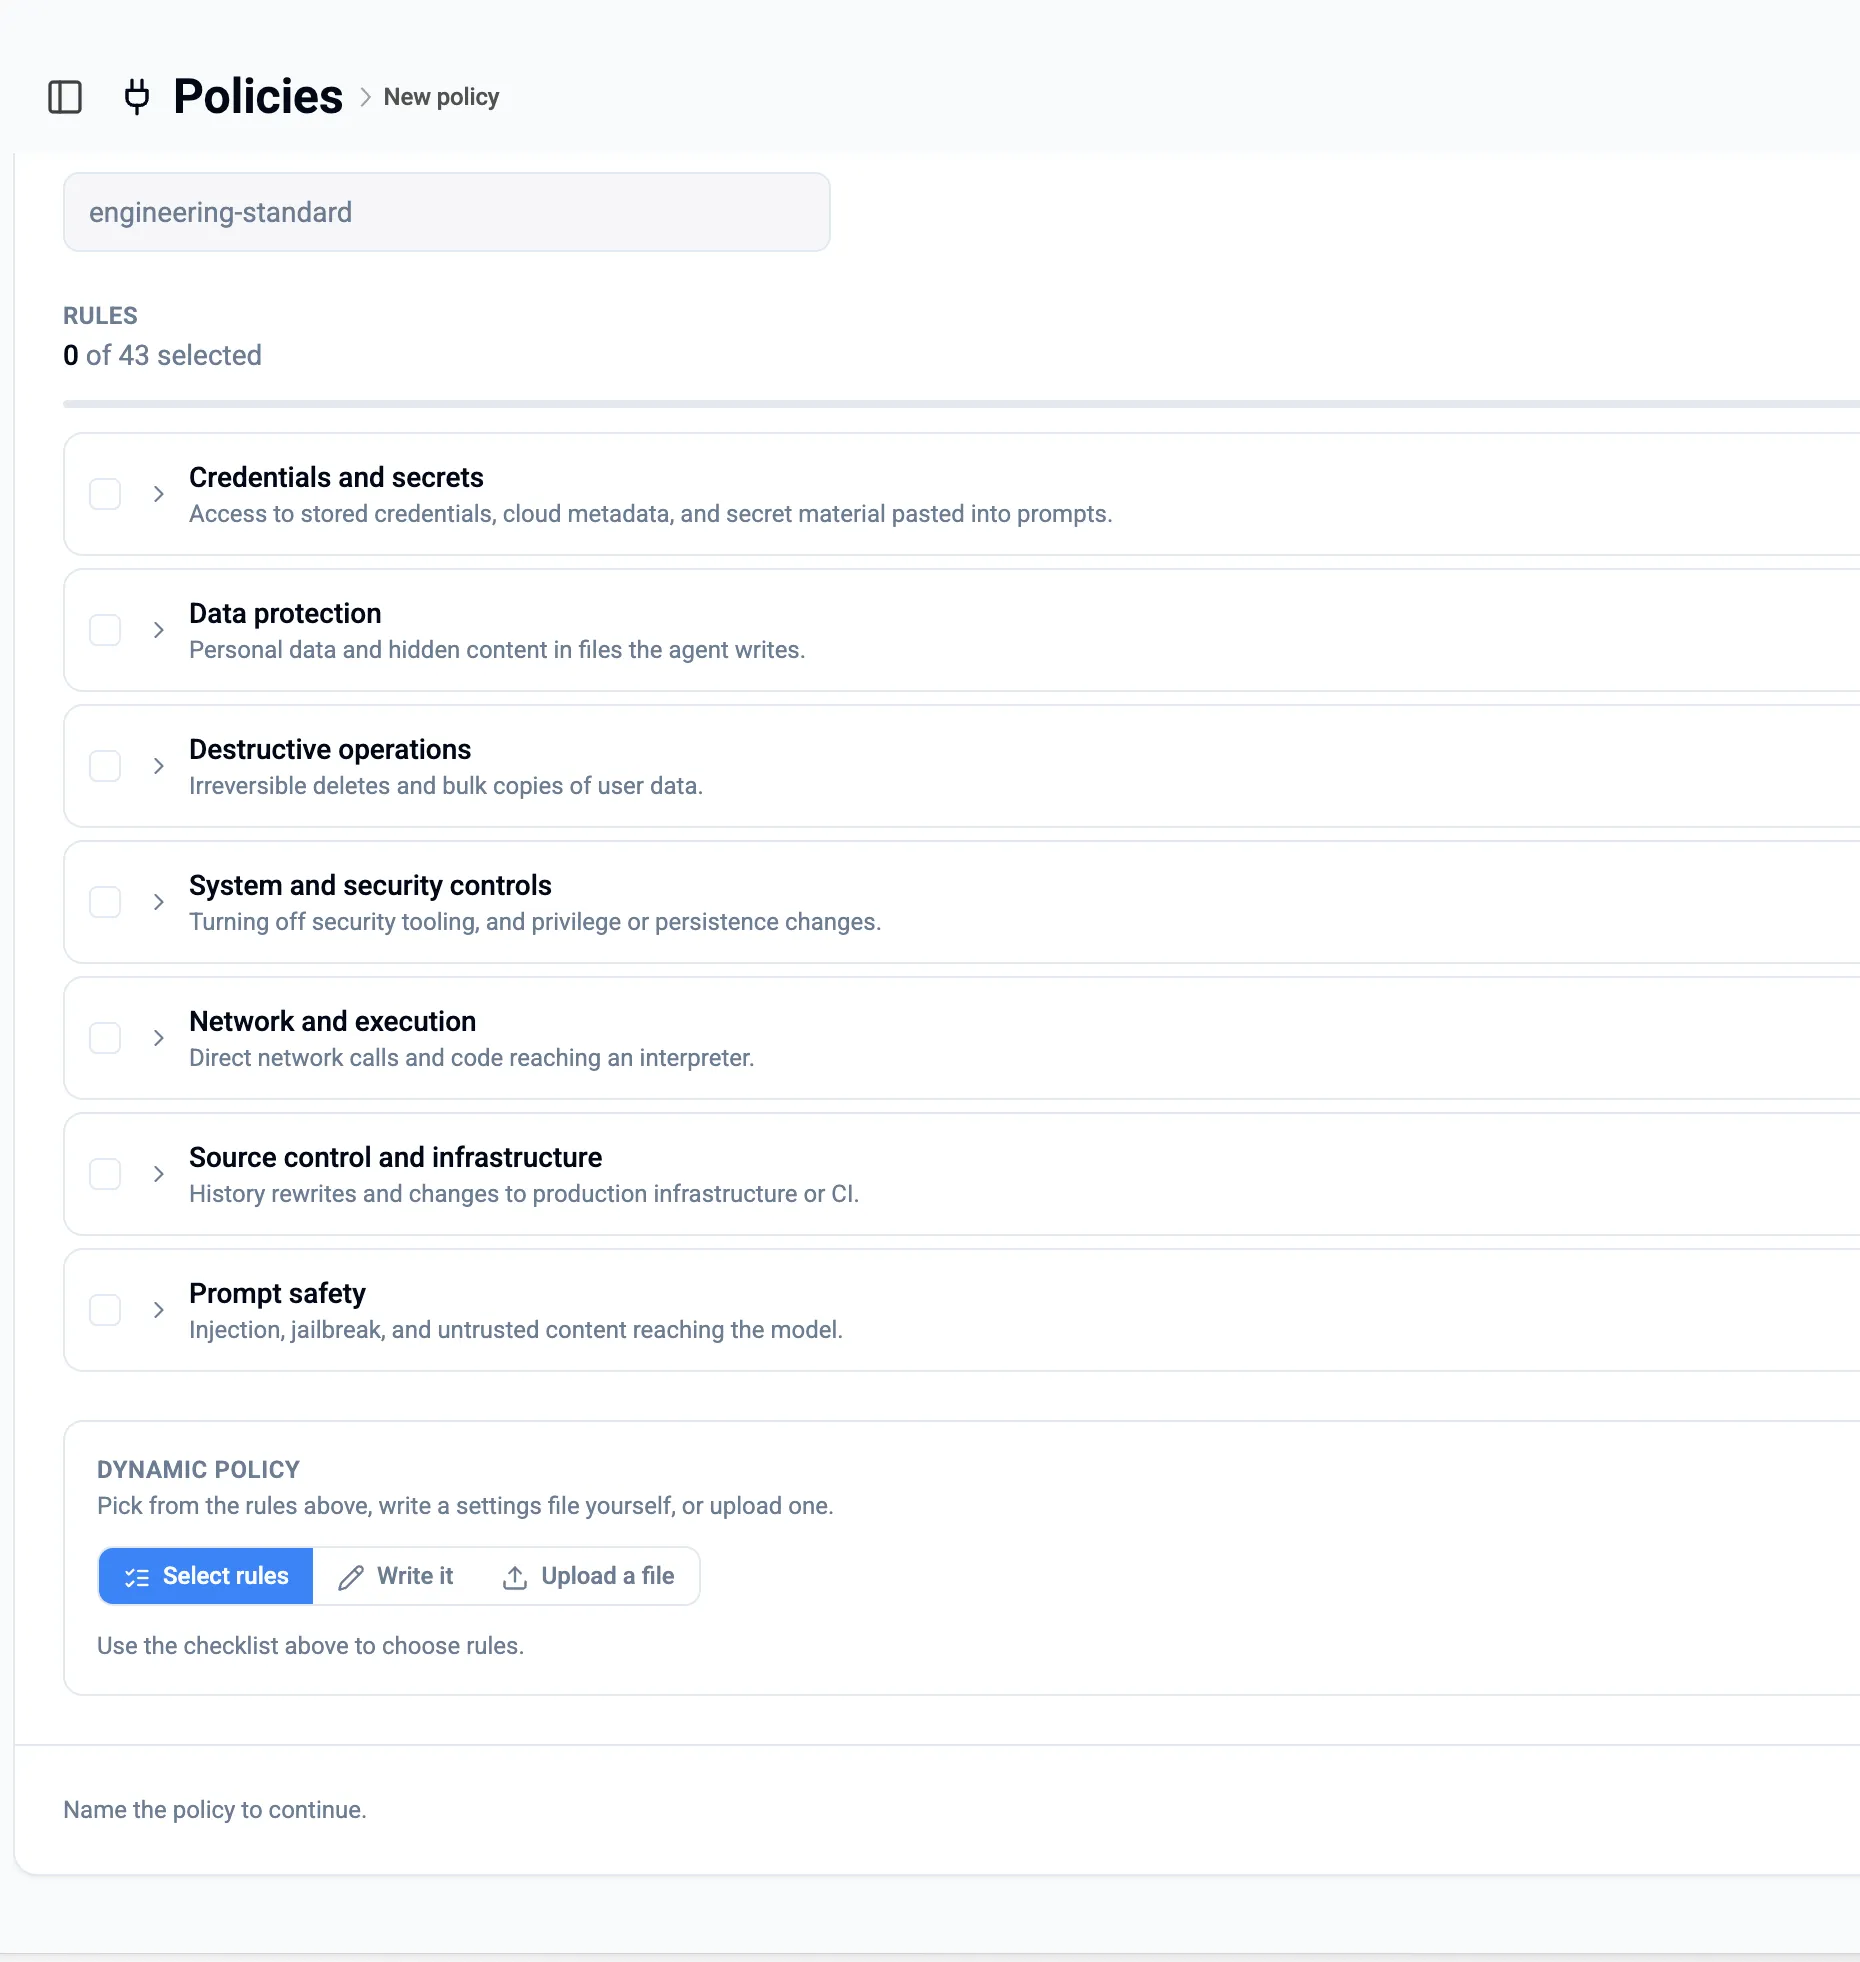
AIBound sets the rules in plain English and the agent enforces them, so the policy applies at the moment of the action.
-
Write the rule in plain English
Your admin types the rule the way they would say it. AIBound turns it into a policy and checks it before it goes out.
-
Apply it to a company, a team or one device
Roll the policy out on Mac and Windows. AIBound safety defaults are always on, and every change can be rolled back.
-
The agent enforces it on every action
Each action is allowed, asked about or denied in real time. Users cannot switch the policy off.
Data classes
Six kinds of data, six ways it leaves through AI.
Each kind of data leaves through AI in a different way. AIBound sets a policy for each one, inside the agent.
What you get
Policy that keeps data in and lets employees keep working
Allow what is safe, ask about what is risky and deny what is not. Employees keep their AI tools.
What this looks like in practice
A retailer safely unblocked 210 employees with one policy.
Which products
Which products do this
Three AIBound products keep data inside the boundary.


FAQ
Frequently asked questions
What is AI data leakage?
AI data leakage is sensitive data leaving the company through AI: an agent that reads a secret, a prompt that carries customer data, or a tool call that posts to an outside host. It is hard to see because it happens on the device and inside the agent, not as a file upload.
How do I prevent data leakage through AI agents?
Enforce policy inside the agent. AgentHarness lets an admin write a rule in plain English, such as no reads of SSH keys and a question before any force-push. Each action is then allowed, asked about or denied in real time, so the rule applies at the moment the agent acts.
How is AI DLP different from my current DLP?
Current DLP watches data in use, in motion and at rest, such as email, files and uploads. AI DLP works inside the agent, where the data is read and the action is taken. AIBound adds that layer on the device. Keep your current DLP for the channels it already covers.
Does it inspect the browser or read what employees type?
No. AIBound enforces inside the agent on the device, not inside the browser. In the browser it can detect AI use, but it does not read page content and does not block there. The AIBound Secure Client collects tool metadata only, with no PII or PHI.
Can employees still use AI tools?
Yes. The policy decides what is allowed, what needs a question before it runs and what is denied. Safe actions go ahead without friction. A retailer used one policy to safely unblock 210 employees, so AI stayed in use and the risky actions stayed out.
More solutions
