
Solution · Stop
AI agent security: control what every agent can reach and do
AI agents act with an employee's access. They read repos, call tools and reach production systems. AIBound finds the agents on every employee device, shows what each one can reach, and sets rules inside the agent, so the high-risk actions are stopped in real time, before they happen.
Customer result
145 poisoned skills caught at install.
The problem
How do you secure an AI agent that acts with an employee's access?
A developer starts a coding agent, and it can reach whatever the developer can. Security finds out later, if at all.
How we solve it
Agentic AI security on every employee device
AIBound works on the device where the agents run, so it can see them, map what they reach and set the rules they follow.
-
Find every agent
AISeeker finds the coding agents, desktop assistants and personal agents on each device, with the person who runs each one. Install takes 15 minutes.
-
See what each one can reach
AgentTracer maps who or what each agent runs as, what it is wired into and how far it could go.
-
Set the rules
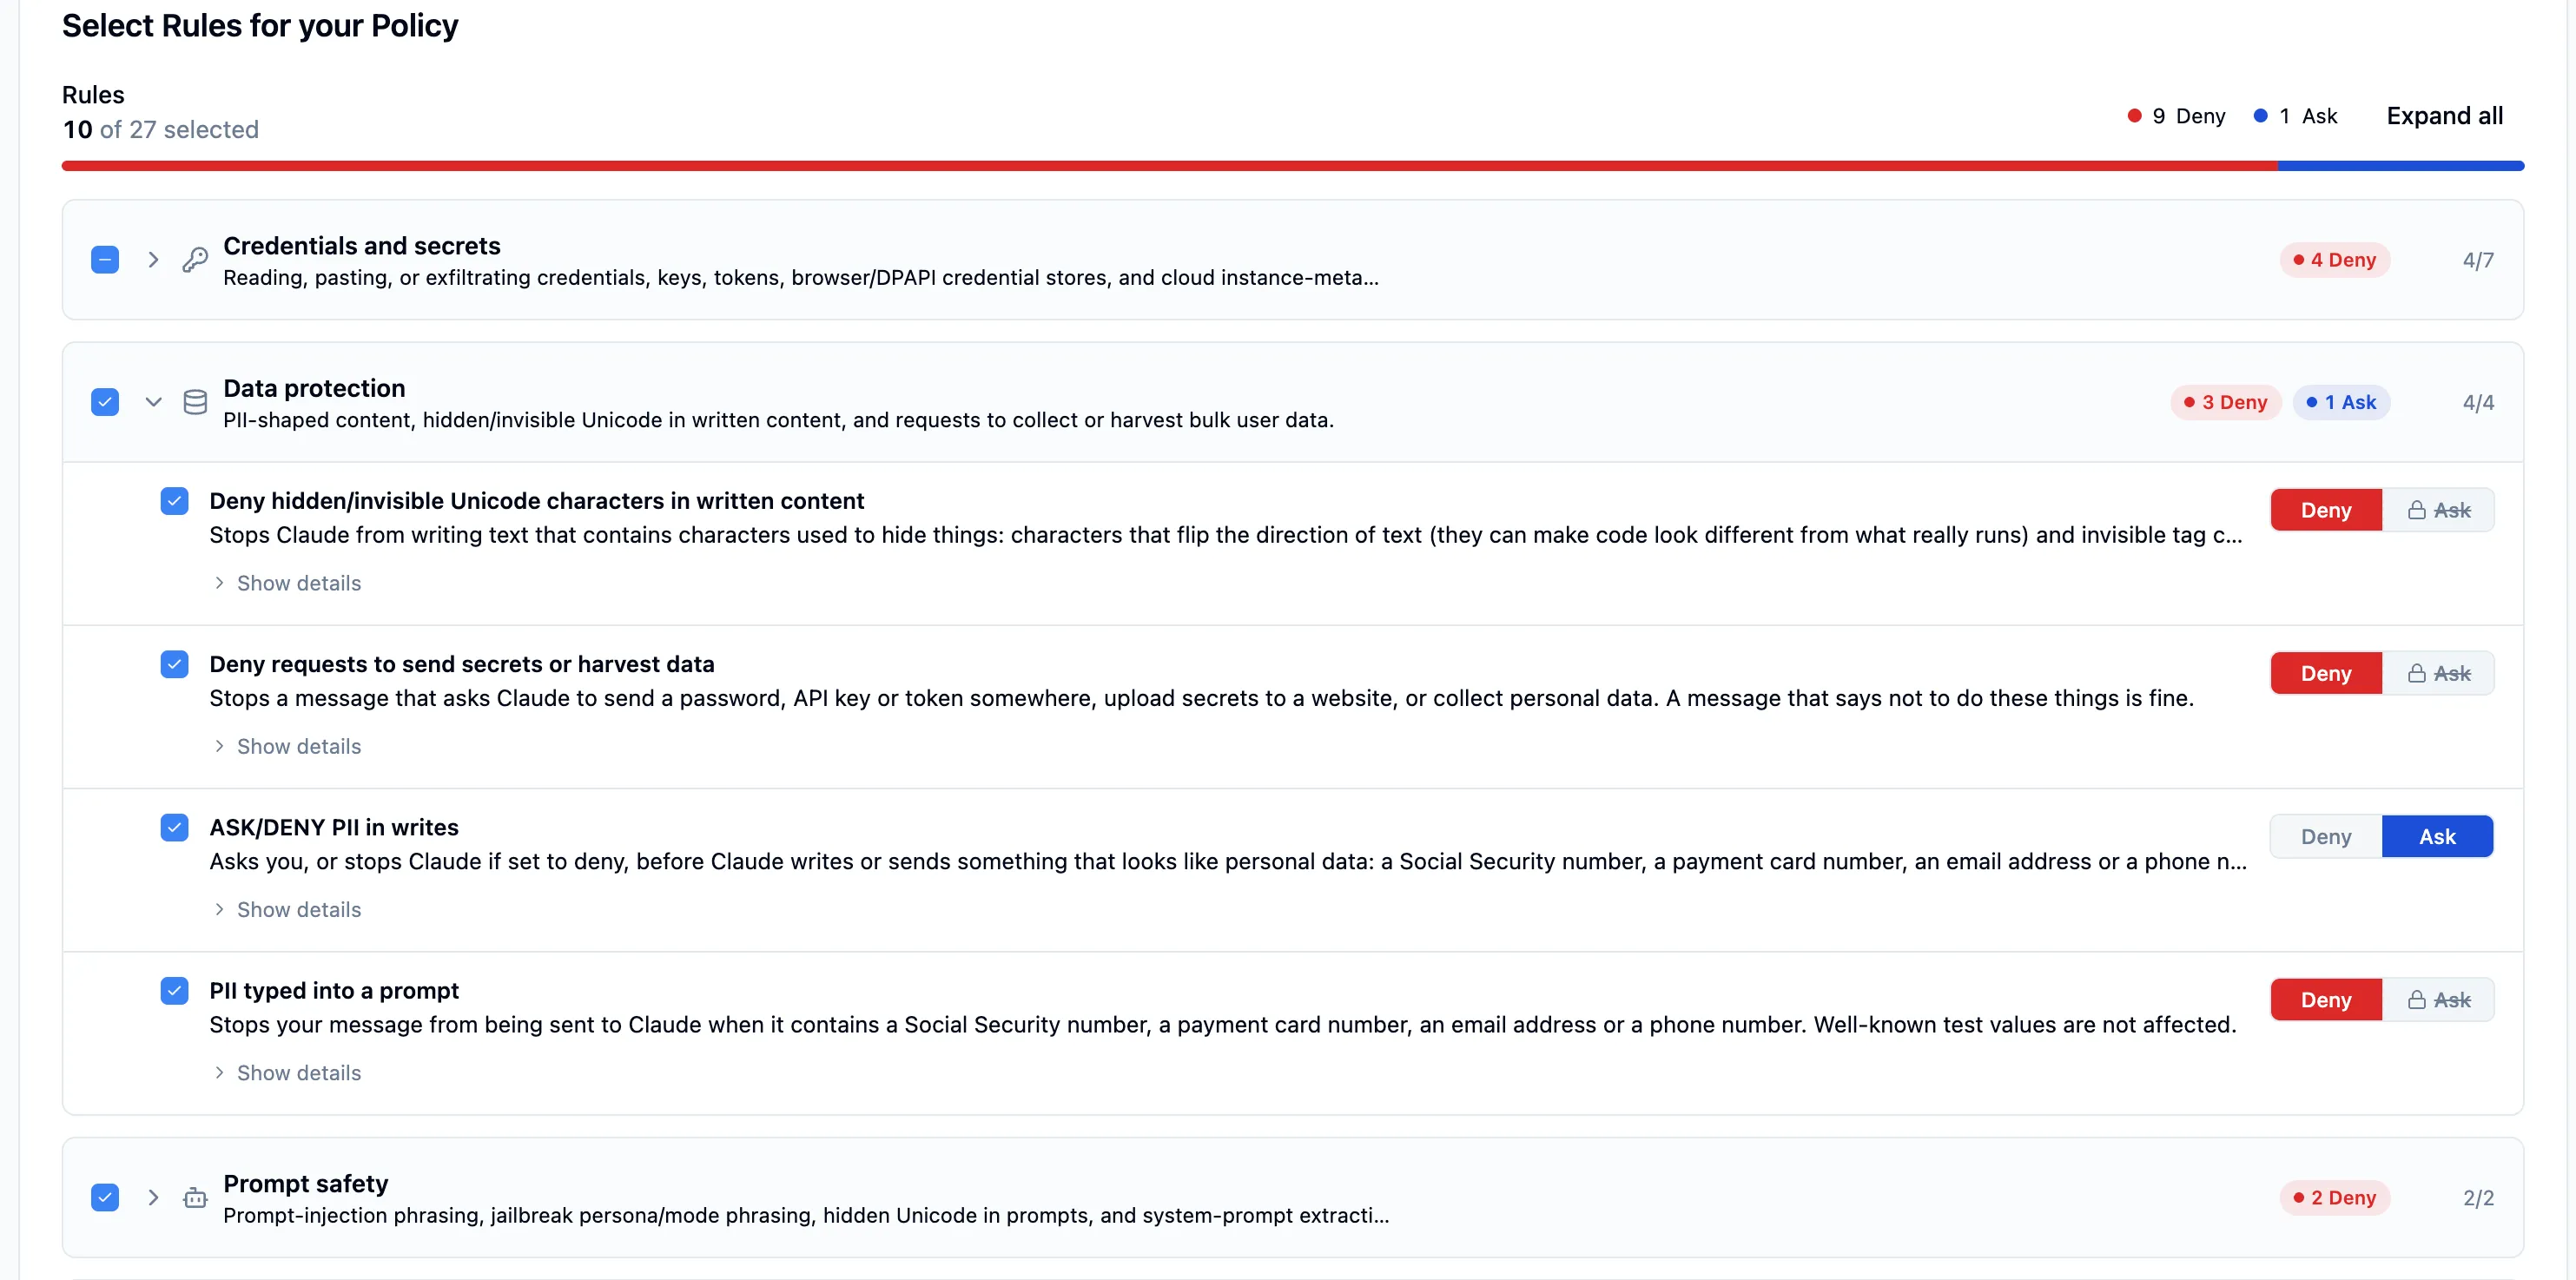
AgentHarness enforces policy inside the agent: each action is allowed, asked about or denied, in real time.
What you get
Every agent under rules you set, in real time
Each finding shows what the agent is, what it can reach and what it is allowed to do. Then you set the rule.
What this looks like in practice
We didn't know 47 employees were running it. AIBound flagged it and blocked it the same afternoon.
A CISO at a European bank.
Which products
Which products do this
Four AIBound products secure agents together.
 AISeeker Finds every AI agent on employee devices, and who runs it. See AISeeker →
 AgentTracer Maps who or what each agent runs as, and how far it could reach. See AgentTracer →
 AgentHarness Enforces policy inside the agent: allow, ask or deny. See AgentHarness →
 SkillGuard Reads every skill like an attacker and blocks the risky ones at install. See SkillGuard →
FAQ
Frequently asked questions
What is AI agent security?
AI agent security is how a company controls the AI agents its employees run: coding agents, desktop assistants and personal agents. It covers what each agent is, what it can reach and what it is allowed to do. AIBound does AI agent security on the employee device, in real time.
Is agentic AI security the same as AI agent security?
Yes, in practice. Agentic AI is AI that acts for a person: it plans steps, calls tools and changes things. Agentic AI security and AI agent security both mean controlling what those agents can reach and do. AIBound does it on the employee device, where the agents run.
How do I stop AI agents reaching sensitive systems?
First, see what each agent can reach. AgentTracer maps who or what an agent runs as, what it is wired into and how far it could go. Then set the rule. AgentHarness enforces policy inside the agent, so each action is allowed, asked about or denied in real time.
What can a compromised AI agent access?
A compromised AI agent can reach whatever its employee can reach: repos, cloud consoles, tokens, and HR or finance systems. AgentTracer maps that path, from the person through the agent's identity and connectors to the data. It maps and does not block. AgentHarness and SkillGuard do the stopping.
How do I stop an AI agent from running a dangerous command?
Set a policy. AgentHarness enforces plain-English rules inside the agent, so each action is allowed, asked about or denied in real time. A destructive command or a credential read can be denied outright. Users cannot switch the policy off, and an AI Kill Switch stops a rogue agent everywhere.
What is AI agent governance?
AI agent governance is how a company sets the rules for the AI agents its employees run, and proves they are followed. You choose the policies, and AgentHarness applies them to every action. AIAssure records each decision as evidence for your GRC program, mapped to the EU AI Act, NIST AI RMF and ISO/IEC 42001.
More solutions
